Cyber agency warns of high-severity TeamViewer flaw
The advisory says CVE-2026-111585, scored 8.8 out of 10, affects clients before version 15.83 on Windows, Linux and macOS and can allow remote code execution.
Pakistan's cyber emergency response team has issued an urgent advisory about a high-severity TeamViewer vulnerability, warning that attackers could crash systems or run malicious code on machines that join a compromised remote session. TechJuice reported the advisory on 11 November, naming the agency as PKCERT in its headline and NCERT in its text.
The flaw is tracked as CVE-2026-111585 and carries a CVSS score of 8.8 out of 10. It affects TeamViewer clients running versions earlier than 15.83 on Windows, Linux and macOS. The affected products include TeamViewer Full Client and TeamViewer Portable for Windows, clients for Linux and macOS, some Android remote-control applications and legacy release branches. Users on 14.x releases should move to 14.7.48868, and those on 13.x to 13.2.36231.
The fault sits in the component that processes remote-control screen data, where an integer overflow can corrupt memory under specific conditions. Exploitation requires the victim to connect to a remote-control session hosted by an attacker-controlled or compromised machine. That condition puts organisations relying on remote technical support, system administration and external IT connections at the most risk.
According to the advisory, the consequences go beyond a single machine. Where remote-access software manages critical systems, one exploited session could expose an entire network, threatening the confidentiality, integrity and availability of affected endpoints. How far an intrusion spreads depends on system configuration and the privileges available to the compromised process.
Organisations that cannot patch immediately were advised to block untrusted outbound remote connections and restrict exposure of vulnerable systems until updates are applied. The agency also recommended allowing incoming and outgoing connections only to approved IP addresses, authorised users and trusted devices. Administrators were asked to review unattended access settings, authentication controls and user permissions, and to grant administrative privileges only where operations require them.
Monitoring should cover TeamViewer connection records, authentication events and endpoint security alerts. Unusual remote sessions, repeated software crashes, unexpected process activity and unauthorised connections are listed as warning signs, though the agency said these do not on their own confirm exploitation and should be investigated alongside other security data.
If a compromise is suspected, organisations were told to assess affected devices and remote-session histories, restrict or disable remote access where needed, preserve security logs for investigation and seek specialist incident-response help where arbitrary code execution or wider endpoint compromise appears likely.
The advisory cites TeamViewer's own Security Bulletin TV-2026-1011 and a corresponding advisory from the Canadian Centre for Cyber Security. TechJuice reported that remote-access tools are widely used in Pakistan by corporate IT departments, managed service providers and freelance technical support workers.
PKCERT warns government and banks of critical Node.js flaws
The national cyber response team says the vulnerabilities allow remote code execution and TLS certificate bypass in Node.js versions 22.x, 24.x and 26.x.

Government assures phased cut in petroleum levy, says Hafiz Naeem
The Jamaat-e-Islami ameer says nine or ten rounds of talks have been held and his party has given the government a final draft and technical proposals.

Thatta Cement, Fauji Foundation sign deal on Pearl Continental owner
The PSX filing says the restructuring of Pakistan Services Limited needs corporate and regulatory approval, days after Fauji Foundation bought a 19.70% stake.

ADB approves $500m emergency financing for Pakistan disasters
The money sits under the second phase of the bank's Climate and Disaster Resilience Enhancement Program and funds immediate budget support after floods, earthquakes or other calamities.
ADB approves $500m disaster financing for Pakistan
The contingent facility gives Islamabad budget support within days of a flood or earthquake, with the bank putting average annual disaster losses at about $2bn.
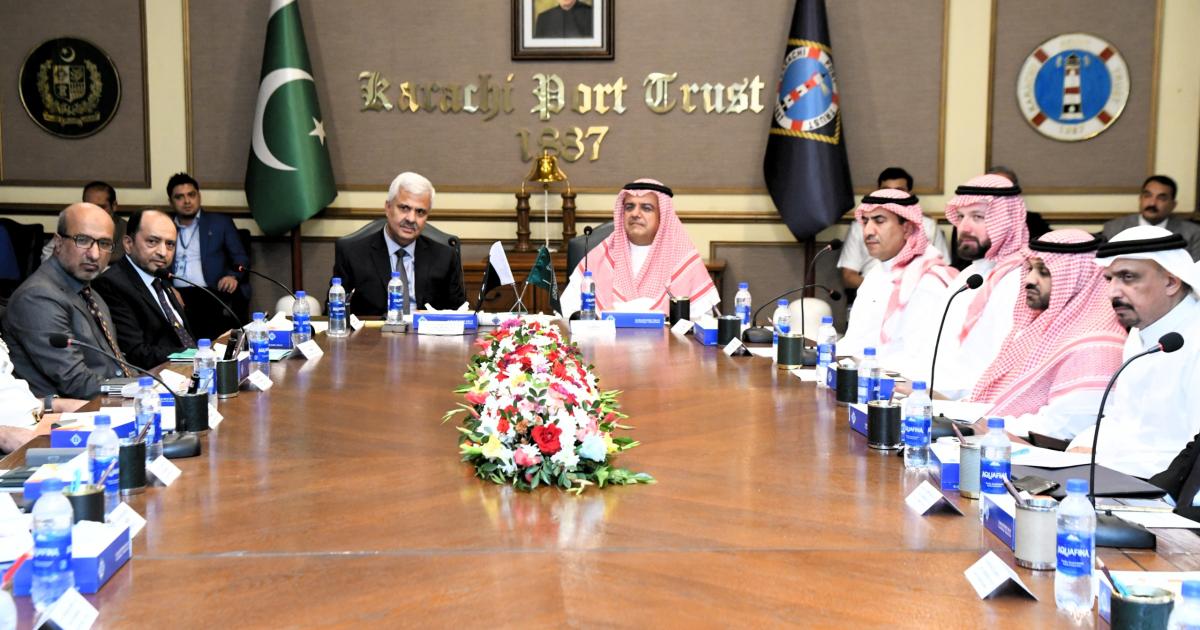
Saudi-Pakistan private equity fund to start at $500m, investors say
Arif Habib, who signed the memorandum for the Pakistani side in Karachi, says regulatory approval will take at least three months before capital is called.
Pakistan Bar Council condemns raids on senator and Quetta bar chief
The council has asked the federal and Balochistan governments and the provincial police chief to identify those responsible and act against them under the law.

Senate panel seeks FBR records over Rs730.8bn tax exemption gap
A subcommittee chaired by Senator Saifullah Abro found imports worth Rs1,120.662 billion recorded under the FATA/PATA scheme but consumption certificates covering only Rs389.865 billion.